SOC live · 24×7

Security operations you'll actually love.

We deliver fully managed cybersecurity, focused on identity, driven by real people, and delivered with full transparency.
16 min
Alert to response, real incident
NPS 90
vs. ~35 industry avg
100%
of alerts investigated, full depth
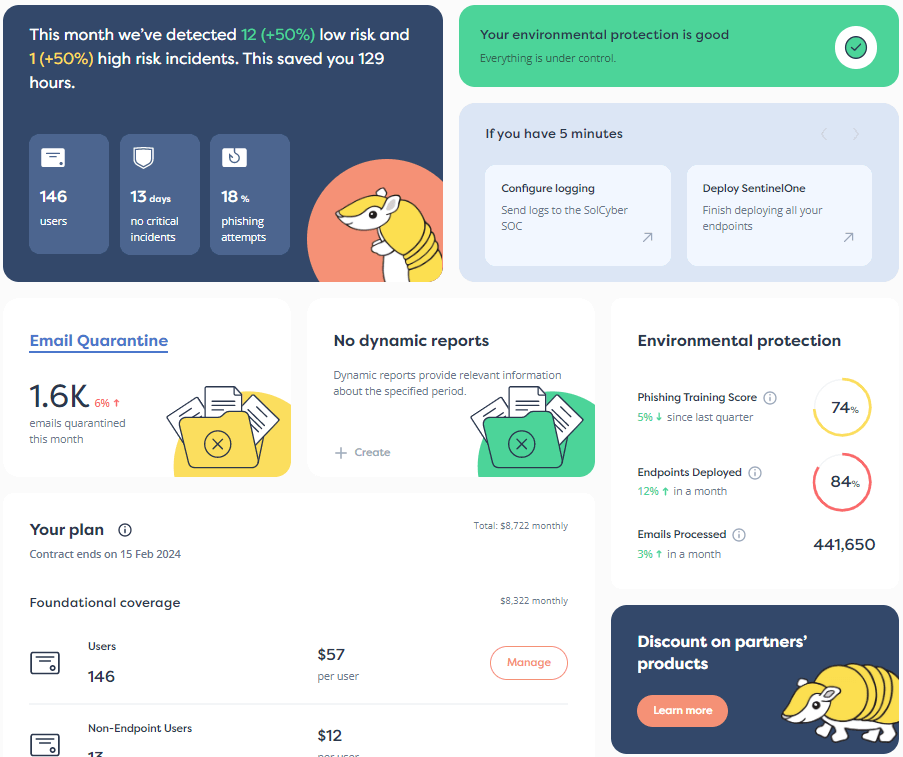
SolCyber Portal — Live Acme Manufacturing
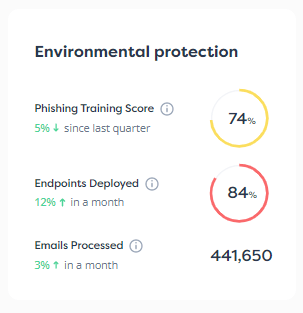
EnvironmentProtected93/93 reporting
Time to triage 30mTime to closure 1h 38m
Impossible-travel sign-intriaged in 0:41 — benign, dismissedCleared
Anomalous OAuth grantAI investigation running — depth 100%Investigating
Malicious inbox rule "_0_"session revoked at 16:09 — pre-breakoutContained
Senior analyst reviewverdict confirmed — customer notifiedHuman
Every alert. Full depth. Nothing tuned out.12,640 today
Attackers break out in 29 minutes. We finish in 16.
Median time to verdict13 min
Alert to response16 min
Alerts investigated100%
Hands-free closures96%

Why customers stay

The Human Experience

Except SolCyber customers. NPS 90 vs. an industry average in the 30s.

We solved the two hardest SOC problems.

A reimagined pipeline and detection thoroughness — unsolved for 20 years.

More time to talk with our people.

50% of SOC interactions are "peacetime" — audit assistance, best practice policies, tool selection. Advice, not just incidents.

"I love my MSSP," said no one ever.
Except our customers.

The industry treats MSSPs as a necessary evil — a ticket wall you shout alerts into. We built the opposite: a named crew, a SOC with no level-1 analysts, and answers from people who know your environment. Customers score it like a product they chose, not a vendor they tolerate.
A named crew that knows your business. CSM, senior analyst, onboarding manager — real people, not a rotation.
Always talking to an expert. The analyst who picks up your case is senior enough to close it.
You talk, we listen. 80%+ of what we build comes from customer requests.
Net Promoter Score — would you recommend your MSSP?
SolCyber customers 90
MSSP industry average 35
Above 70 is considered world-class in any industry.
"We've talked to you more in the first 3 months than the entire 3-year engagement with my previous provider."
ITIT DirectorMid-market financial customer
The AI-native SOC

Two SOC problems went unsolved for 20 years. We rebuilt the SOC around AI and solved both.

Every SOC on earth fights the same two enemies: the pipeline is too slow, and noisy detections get tuned out until the real compromise hides in the silence. Bolting AI on doesn't fix either. Rebuilding around it fixes both.
Solution 1 — Pipeline latency
Reimagined pipeline: alerts skip the hops.
Legacy SOC — alert to response 70 min
SolCyber AI-native 16 min
Attacker breakout: 29 minutes. Only one of these finishes in time.
Solution 2 — Detections tuned out
Full depth on every alert. Nothing silenced.
Low AlertsHigh alertsThe real compromise
What customers use the SOC for
50% peacetime50% incidents
audits · policy · advice · toolingdetections · response
Peacetime requests · this month Included in your program
Evidence pack for SOC 2 auditdelivered · 2 days
"LayerX vs Island?" — tooling advice call30-min call · senior analyst
Incident-response policy templatein progress
Vendor security questionnaire helpin progress
Beyond incidents

Giving you more time to talk with our people.

The average customer sees about one critical escalation a month. So what's your MSSP doing the other 30 days? Because AI clears the alert volume, our people are free for what actually improves your security — and it shows: half of all interactions with our SOC are "peacetime", not incidents.
Phone-a-Friend advisory — unlimited. Any security question, answered by email or a 30-minute call.
Audit & compliance support. We pull the evidence and join the assessor call.
Submitted right from the portal. Peacetime requests live next to your detections — one queue, one crew.
The SolCyber difference

Not another platform to run.

Platform-first MDR gives you a great platform — and leaves the relationship to a ticket queue. We're a managed program built around you.
Platform-first MDR
SolCyber
You deploy, configure, and confirm the tooling is actually working
We manage everything — and make sure it's working
A "we call you, don't call us" SOC
Call us anytime — half our interactions aren't even incidents
Every human interaction outside the SOC is a sales call
A named crew who know you — advice included, never a pitch
One-size-fits-all: you adapt to the platform's way of working
We adapt to your processes and your environment
Total transparency

Everything we do, visible in your portal.

Every detection, every verdict, every analyst note — with as much visibility as you want. No black boxes. We call it OmniView.
OmniView portal dashboard on a laptop

What customers say

"You're my favourite vendor to work with — and we have dozens."
CTCTORetail, 1500 employees
"The portal continues to change every quarter; I love that our feedback is getting heard."
ITHead of ITLogistics, 500 employees
"Pedigree of the largest providers but with love, care and passion from a startup."
CICIOServices, large enterprise

See the SOC and the portal, live.

A 30-minute walkthrough with the people who'd run yours. Full coverage in 30 days, no upfront onboarding costs.

Follow us!

Subscribe

Join our newsletter to stay up to date on features and releases.

By subscribing you agree to our Privacy Policy and provide consent to receive updates from our company.

©
2026
SolCyber. All rights reserved
|
Made with
by
Jason Pittock

I am interested in
SolCyber DPM++

I am interested in
SolCyber XDR++™

I am interested in
SolCyber MDR++™

I am interested in
SolCyber Extended Coverage™

I am interested in
SolCyber Foundational Coverage™

I am interested in a
Free Demo

109